Create an assumable identity for a CLI session authenticated with Keycloak
Procedural tutorial outlining how to create a Chainguard identity that can be assumed by a Keycloak user.
8 min read
For the complete documentation index, see llms.txt.
This guide walks you through the Chainguard Console. Anyone can use the Console, but you first need to create an account and log in.
If you’re not ready to create a Chainguard account, you can follow along with the public Chainguard Directory. It offers similar information, but it isn’t connected to an organization or account. The directory’s Sign In link opens the Console.
Log in to access the Chainguard Console.
To open the Console with your organization already selected, use (and bookmark) a link like this one, replacing ORGANIZATION with your organization’s name:
https://console.chainguard.dev/auth/login?org=ORGANIZATIONTo learn about browsing Chainguard Libraries in the Console, refer to the Libraries browsing page.
When you sign in to the Chainguard Console, it opens to the Overview page:
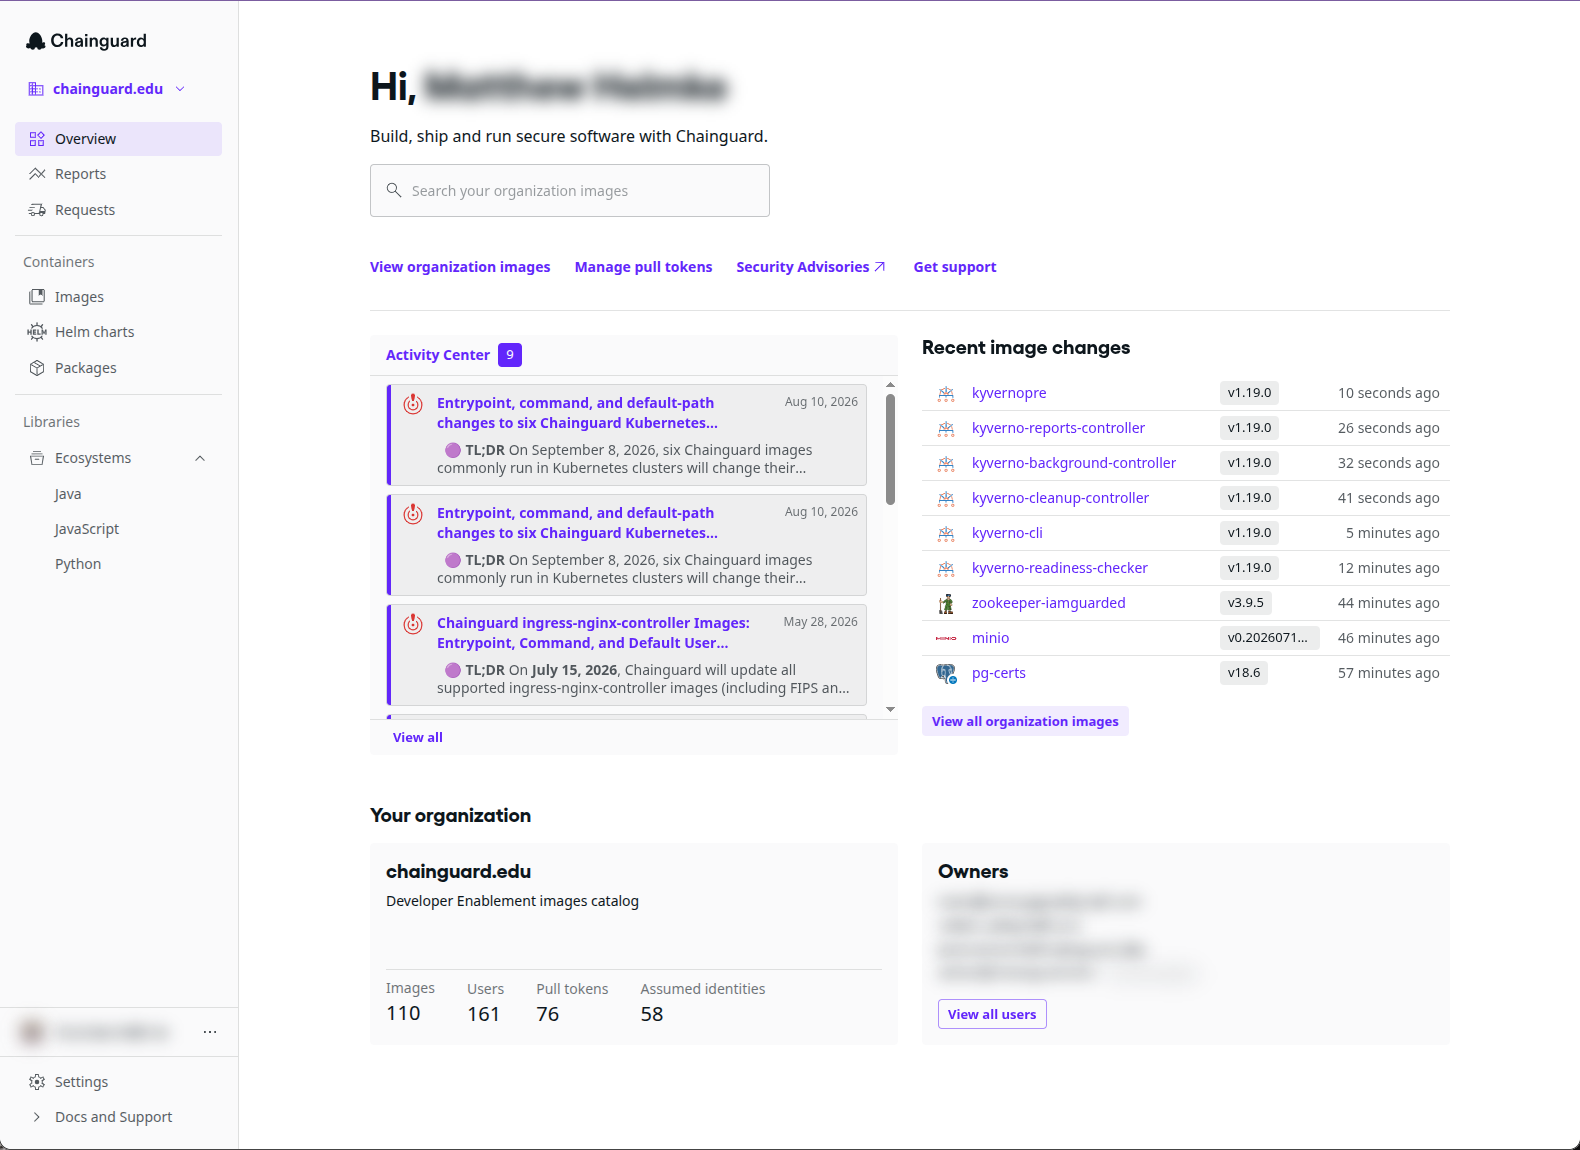
If your organization and account have Chainguard Notifications enabled, this page also shows the Activity Center, where Chainguard posts occasional notifications.
Click Images in the left-hand navigation. The Images page opens to the Organization tab. If you’re part of an organization, this tab lists the private Chainguard Containers (also called Production Containers) your organization can access.
Select the Chainguard catalog tab, which lists all of Chainguard’s available images in a table with four columns:
If you belong to an organization, this tab also has an unlabeled column with an Add to org button for each image. For images already in your organization, the button has a different icon and adds another instance of the image. Depending on your organization’s plan, some images might show a different option instead, such as Contact us. With catalog pricing, Add to org lets you provision Chainguard Containers yourself, without contacting Chainguard. For more information, refer to Chainguard container catalog pricing.
If an image you need doesn’t appear in your organization’s catalog, or appears without the version you need, refer to Troubleshoot container and version availability.
The Organization tab has no Description column, but it adds two others:
docker pull command.Click a column name to sort the list by that column, in ascending or descending order.
Above the table, a search box finds images by name or latest version number. To its right, the Filter by menu filters the images by their container image category.
Click any container image to open its details page:
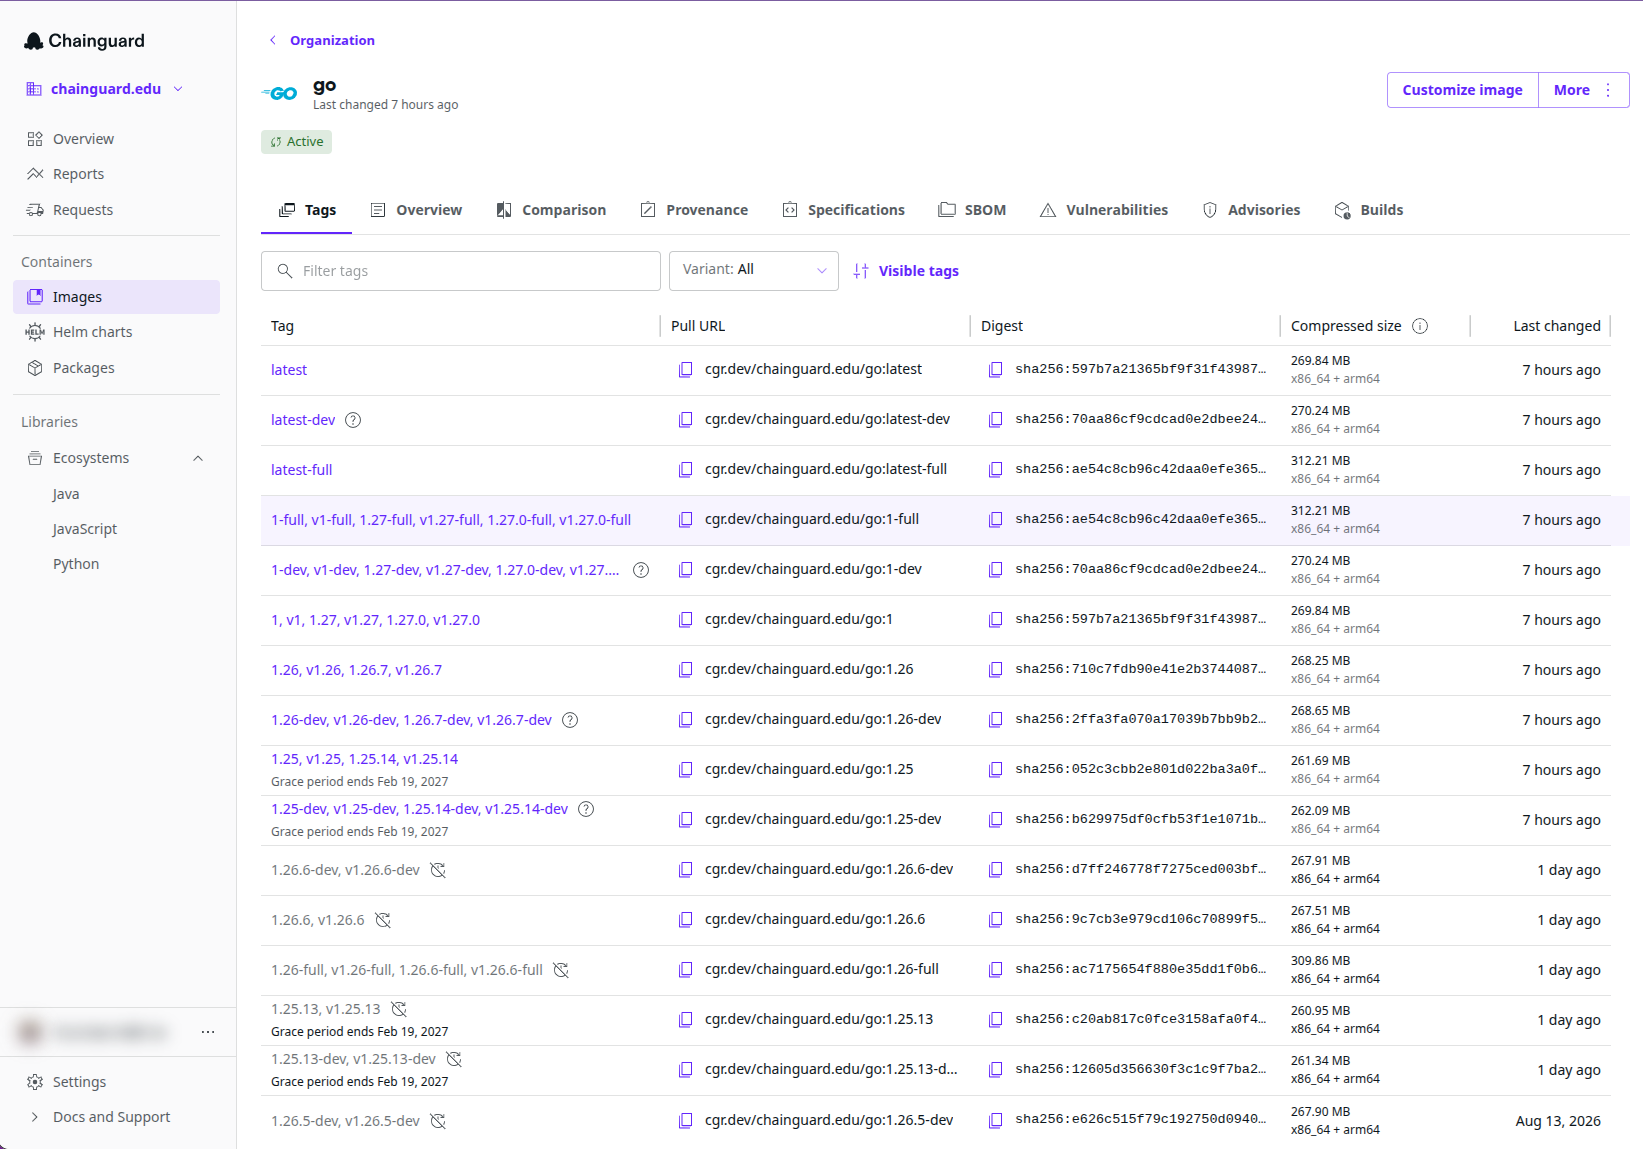
This example shows the details page for go in the Console.
Each image’s details page has several tabs, each covering a different aspect of the image.
Each image opens on the Tags tab, which lists the image’s version tags in a table with these columns:
Above the table, a search box filters the image’s versions. A Variant drop-down menu filters for all images, only development variants, or only non-development variants.
The Overview tab contains the container image’s README. READMEs typically explain how to download the image, note any compatibility issues, and describe how to get started with it.
The Comparison tab compares the CVE count of a Chainguard Container with a non-Chainguard alternative, with charts that visualize the comparison. For more information, refer to CVE visualizations.
All Chainguard Containers contain verifiable signatures and high-quality software bills of materials (SBOMs). Signatures let you confirm each image’s origin, and SBOMs list everything the image contains.
The Provenance tab explains how to verify container signatures and how to download and verify image attestations, with examples that use cosign.
The Specifications tab lists important details about the image, such as whether it ships with the apk package manager or a shell, its default user ID, its environment variables, and its entrypoint.
It also shows the image’s Raw configuration, which includes many of these details plus the image’s OCI labels (similar to annotations).
The SBOM tab lists the packages in the image. Everything in a Chainguard Container is a package, so this list is a complete view of the image’s contents.
The package table has six columns:
golang or apkAbove the table, a search box filters the package list. To its left, two drop-down menus select the image version and the architecture (x86_64 or arm64) whose SBOM you want.
To the right of the search box, the Download button downloads the SBOM in SPDX or CycloneDX format. It’s available for Free Containers and for images your organization has access to.
Chainguard began generating SBOMs for its images on November 15, 2023, so image versions released before that date have no SBOM data.
The Vulnerabilities tab lists every CVE found in the image. Like the SBOM tab, it has a search box for filtering the list and, to its left, a drop-down menu for selecting an image version.
Most Chainguard Containers show no vulnerabilities for the latest version. This isn’t an error: Chainguard aims to remove vulnerabilities from images as soon as they arise. To check how the table appears when vulnerabilities are present, select different versions in the drop-down until you find one with a vulnerability.
The table has five columns:
Click the down-pointing chevron (˅) to the left of a row to expand it. The expanded row shows the Package name and Version, the package’s Fixed version, a brief Description of the vulnerability, and one or more References where you can learn more.
As with SBOM data, Chainguard began generating vulnerability data for its images on November 15, 2023, so image versions released before that date have no vulnerability data.
The Advisories tab lists the CVEs that have affected the image and what action Chainguard took on each one. It shows a timeline of the image’s security advisories, newest first. Each entry specifies the date and time the advisory was released, the CVE in question, the affected package, and the current status.
To learn more about Chainguard security advisories, read How Chainguard issues Security Advisories and How to use Chainguard Security Advisories. You can also browse every advisory published for Chainguard Containers on the self-service Security Advisories page.
In the Console, images also have a Builds tab, which lists recent builds of the image. The tab is available only for images with an Active status. It’s especially useful for images customized with Chainguard’s Custom Assembly tool.
For more about the Builds tab and working with Custom Assembly in the Console, refer to Using the Chainguard Console to manage Custom Assembly resources.
For organizations that deploy Chainguard container images with Helm, Chainguard provides upstream-produced Helm charts and a set of Chainguard-created iamguarded charts, designed for organizations migrating off Bitnami.
To find these charts in the Console, click Helm charts in the sidebar menu. The iamguarded charts have an iamguarded label. Click a chart name to open its details.
To find the packages available to your organization, click Packages in the sidebar menu. The Packages page lists the APK packages in your organization’s private Chainguard APK repository, and you can search the list.
Click a package name for more details. Use the Architecture drop-down to choose which architecture to display.
The Chainguard Console helps you find which Chainguard container images are available and learn details about each one. To work with an individual image, check whether a getting started guide exists for it. You can also learn how to use Security Advisories on the self-service public Security Advisories page.
Last updated: 2026-10-05 00:00